SECURITY AND TRUST
Your most sensitive data.
Our most serious commitments.
Visier encrypts and isolates your workforce data, keeps its AI explainable and overseen by people, and verifies both through independent audits and contracts.
THE CHALLENGE
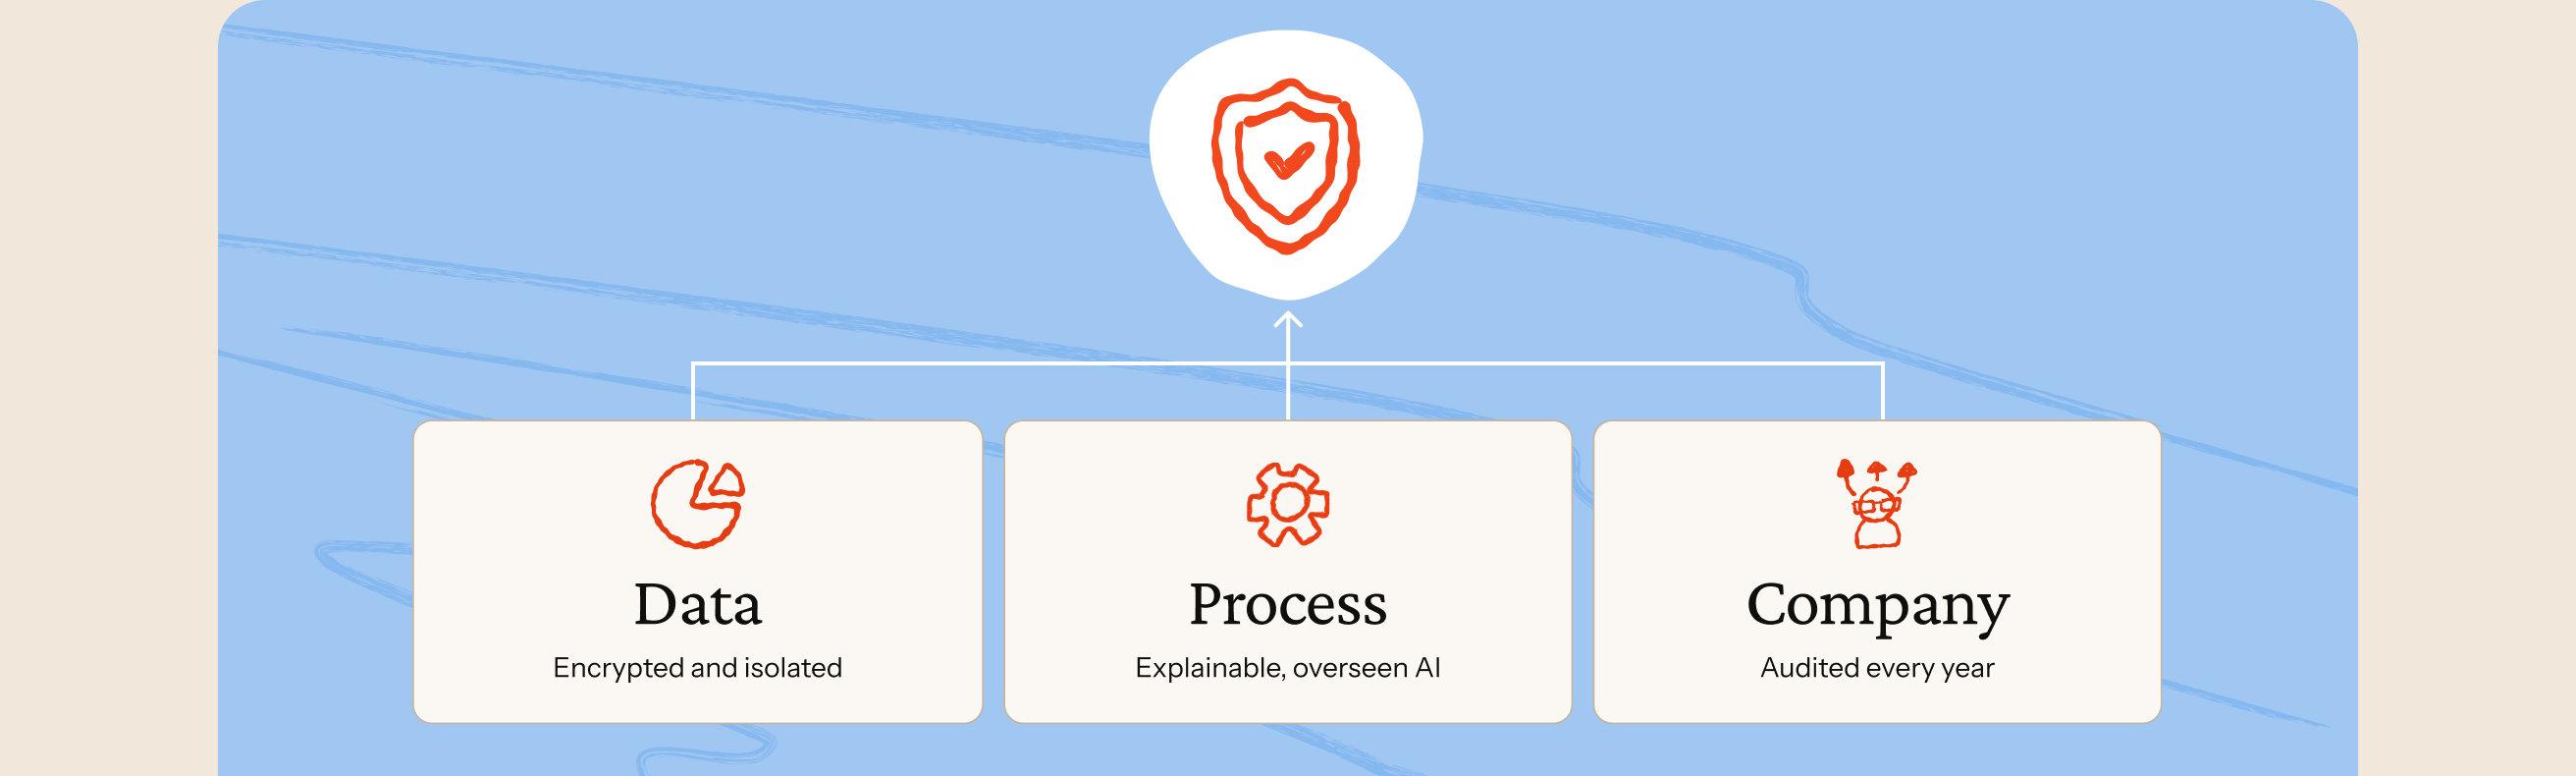
Three ways Visier earns trust
Workforce data is the most sensitive data you hold, and AI raises the stakes. Every agent that queries it is another surface to govern. Visier builds trust in three places.
Trust the Data
Encrypted, isolated, and in your control
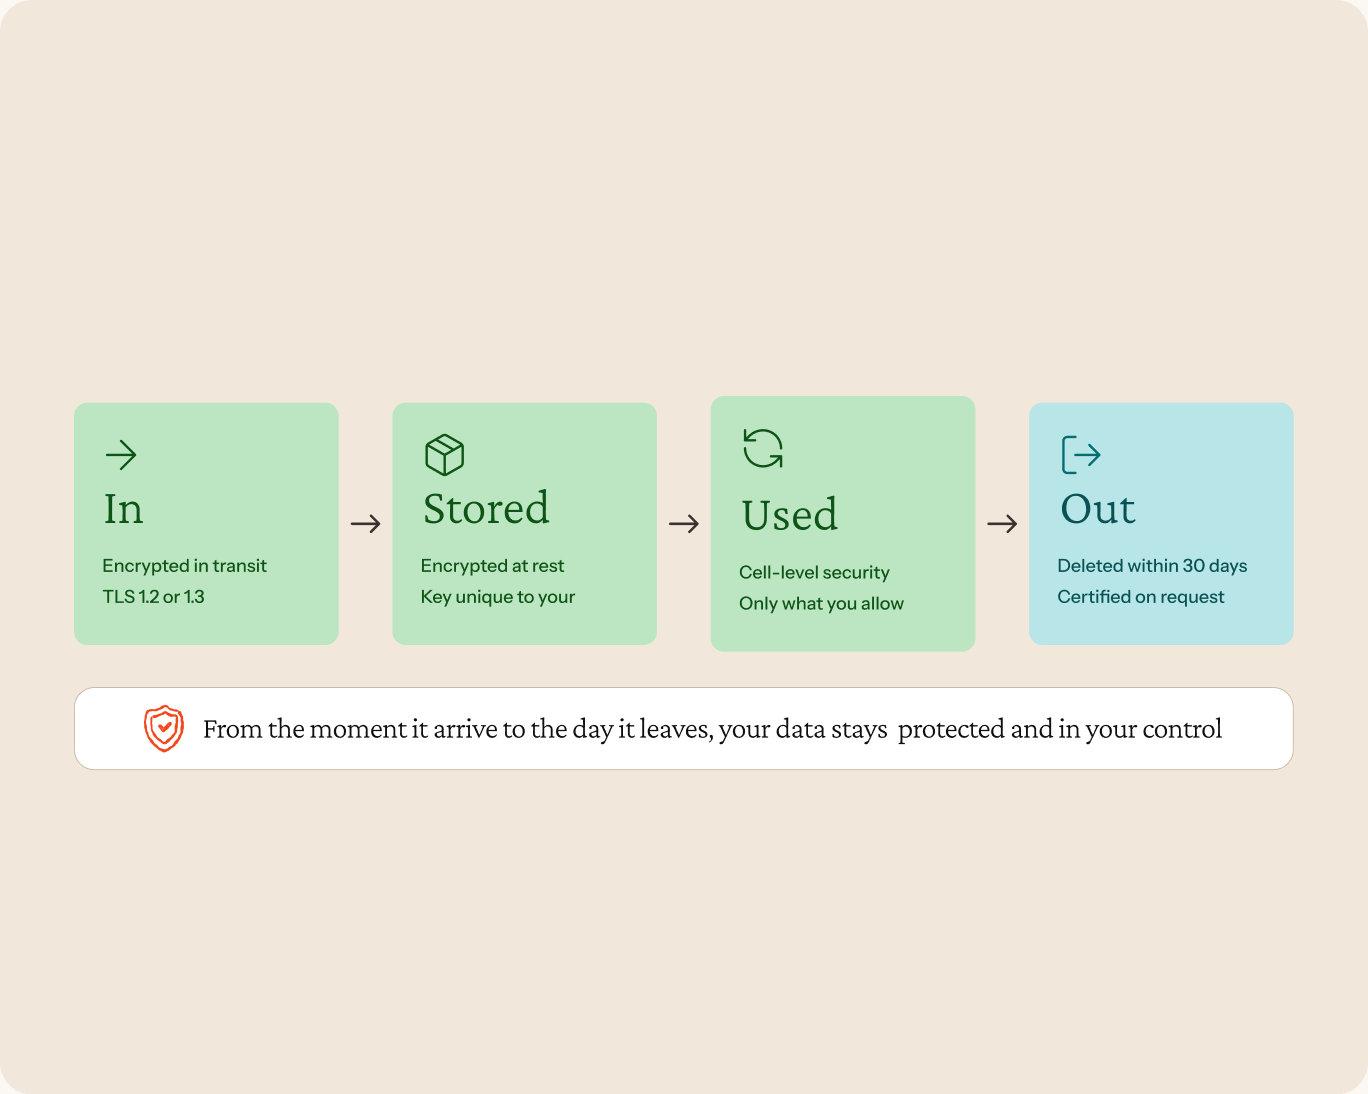
Your workforce data is protected at every layer, and you decide who sees what. It is encrypted with a key unique to you, isolated from every other customer, and stored in the region you choose. Only a small number of trained, background-checked Visier employees can reach it, and our cloud providers cannot read it.
AES 256-bit encryption at rest, TLS 1.2 and 1.3 in transit
Penetration testing by an independent third party at least annually
Data deleted within 30 days when you leave, with written certification on request
Trust the Process
AI you can explain, oversee, and hold us to
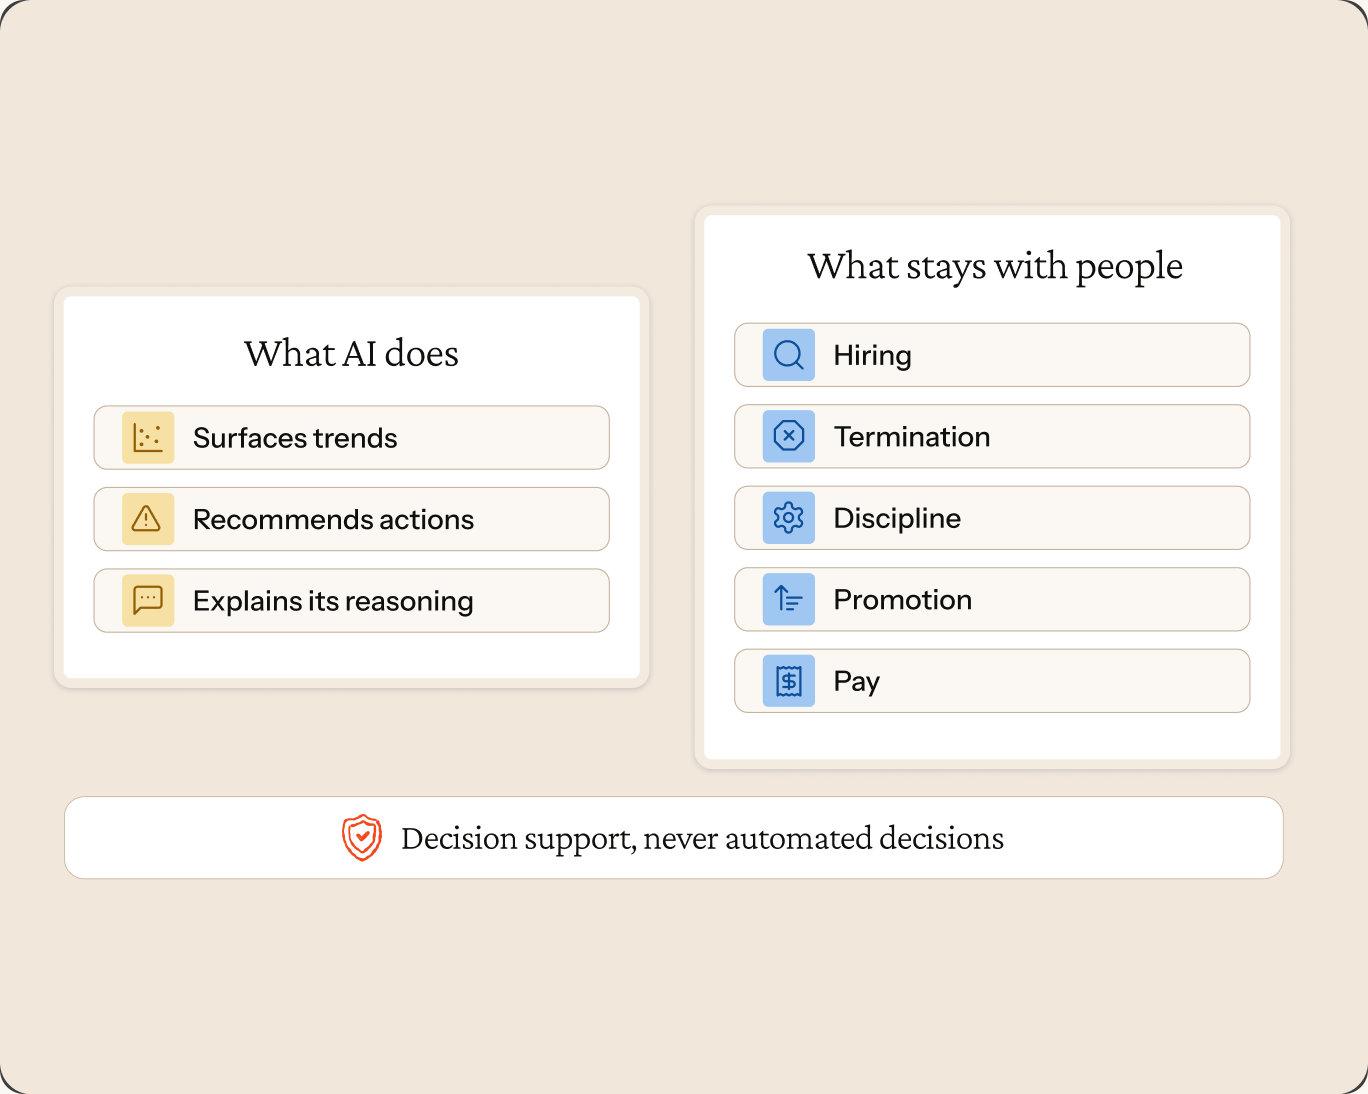
Visier’s Agents and AI is built to show its work and keep people in charge. A cross-functional AI Taskforce oversees how we build and use it, and the commitments are written into your contract through the AI Addendum.
Customer data is not used to train generative AI models
Citations and data summaries show what sits behind an answer, and people can review and override outputs
Visier’s Agents and AI never makes decisions about hiring, termination, discipline, promotion, or pay
Pre-deployment testing and ongoing validation sit inside a continuous risk process, and we track rules like the EU AI Act
Trust the Company
Protecting workforce data for over 16 years
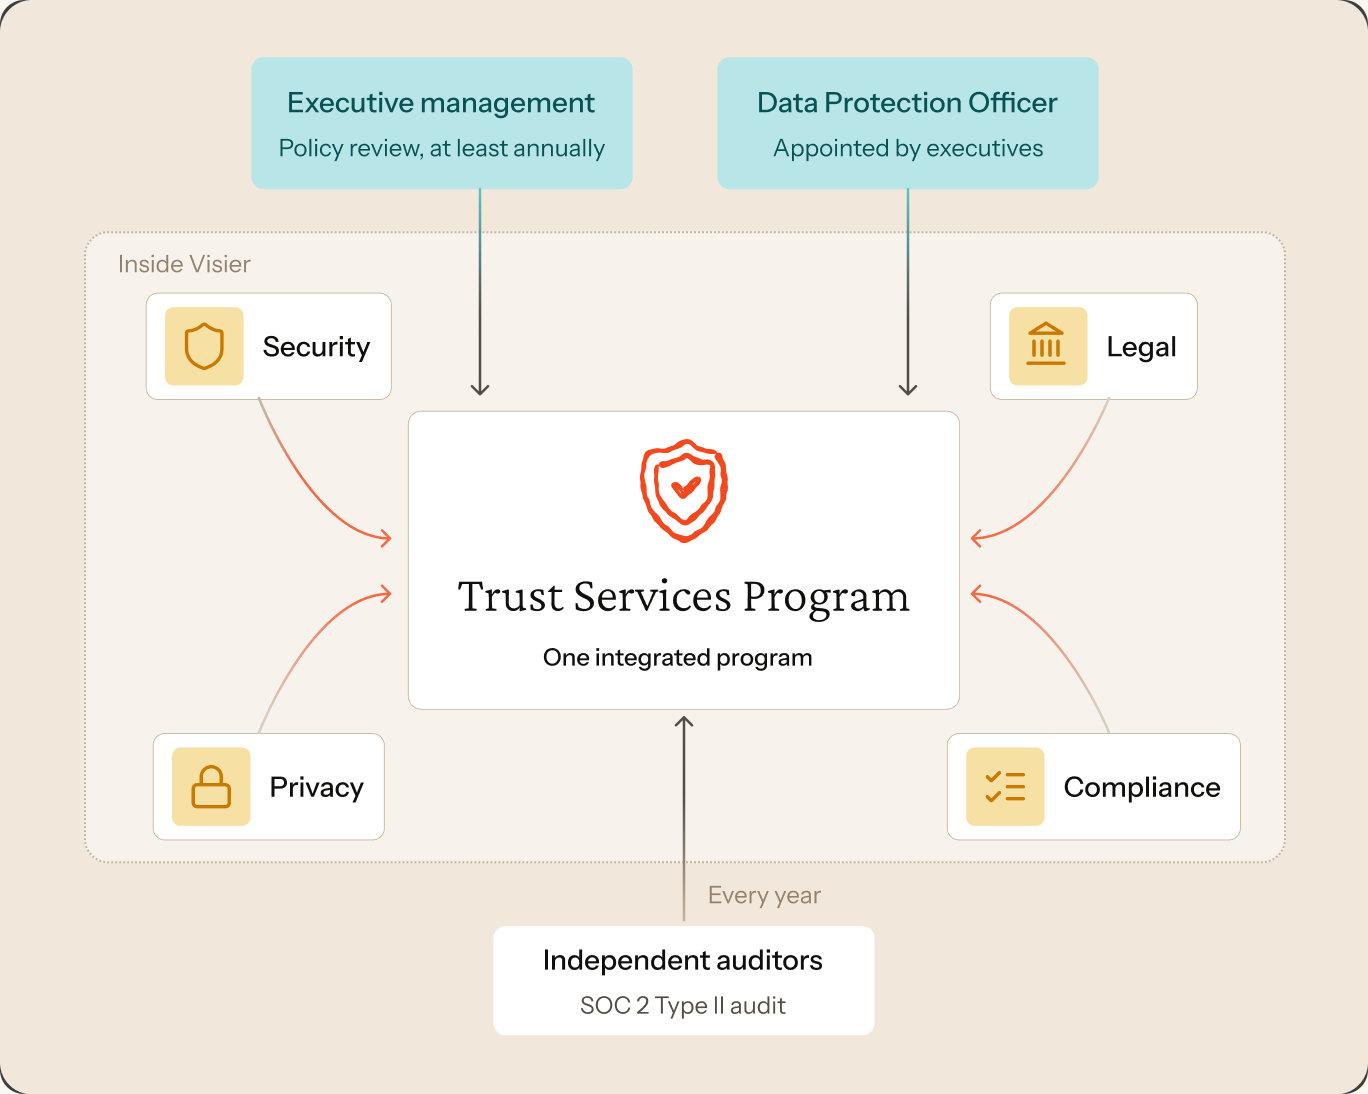
Our Trust Services Program brings security, privacy, legal, and compliance teams together at Visier. Independent auditors check our work every year, and leadership reviews policies at least annually.
SOC 2 Type II audit every year, plus CSA STAR Level 1
A named Data Protection Officer appointed by the executive team
Mandatory privacy training for every employee
A disaster recovery plan that is tested and reviewed annually
Notice of a security incident within 24 hours of confirmation
COMPLIANCE & DATA RESIDENCY
Independently verified. Stored where you need it.
Third-party audits, recognized privacy frameworks, and four data center regions for your residency requirements.
Governed, secure, makes IT happy

FAQ
Does Visier use customer data to train AI models?
Visier does not use customer data to train any generative AI models or technologies. According to Visier’s AI Addendum, customer data processed by Visier’s AI systems is used only for the purposes set out in the customer’s agreement.
Who can access customer data at Visier?
Only a very limited number of Visier employees can access customer data, and only to provide support and manage changes customers request. They complete an enhanced background check and additional training first. Visier’s cloud and data center providers cannot access unencrypted customer data.
Can Visier’s AI make hiring, firing, or pay decisions?
No. Visier’s AI is a decision-support tool. The Visier AI Addendum calls for meaningful human review of AI outputs and prohibits using the AI system for automated decisions about hiring, termination, discipline, promotion, or compensation.
Is Visier SOC 2 Type II compliant?
Yes. Visier completes a SOC 2 Type II audit every year, performed by an independent auditor from an internationally recognized public accounting firm. The report covers the Security, Availability, and Confidentiality trust services categories and typically releases each March.
Is Visier ISO 27001 certified?
No. Visier is not currently ISO 27001 certified. Its security and privacy programs follow the NIST Cybersecurity Framework and ISO 27001, and independent assurance comes from an annual SOC 2 Type II audit and CSA STAR Level 1 status.
Where does Visier store customer data?
Visier operates data centers in Canada, the United States, Germany, and Singapore so customers can meet data localization and residency requirements. The data centers are physically dispersed within each region for redundancy and availability.
Does Visier support GDPR?
Yes. Visier has an appointed Data Protection Officer who oversees its privacy program. It offers a Data Privacy Addendum with Standard Contractual Clauses to every customer who needs one and also relies on the EU-U.S. Data Privacy Framework for transfers.