SECURITY AND TRUST
AI governance that’s built in, not bolted on.
Every AI agent, every API, every user governed by the same model. No separate governance project. No per-channel builds.
ONE GOVERNANCE MODEL ENFORCED AT QUERY
Safely power AI agents with workforce context
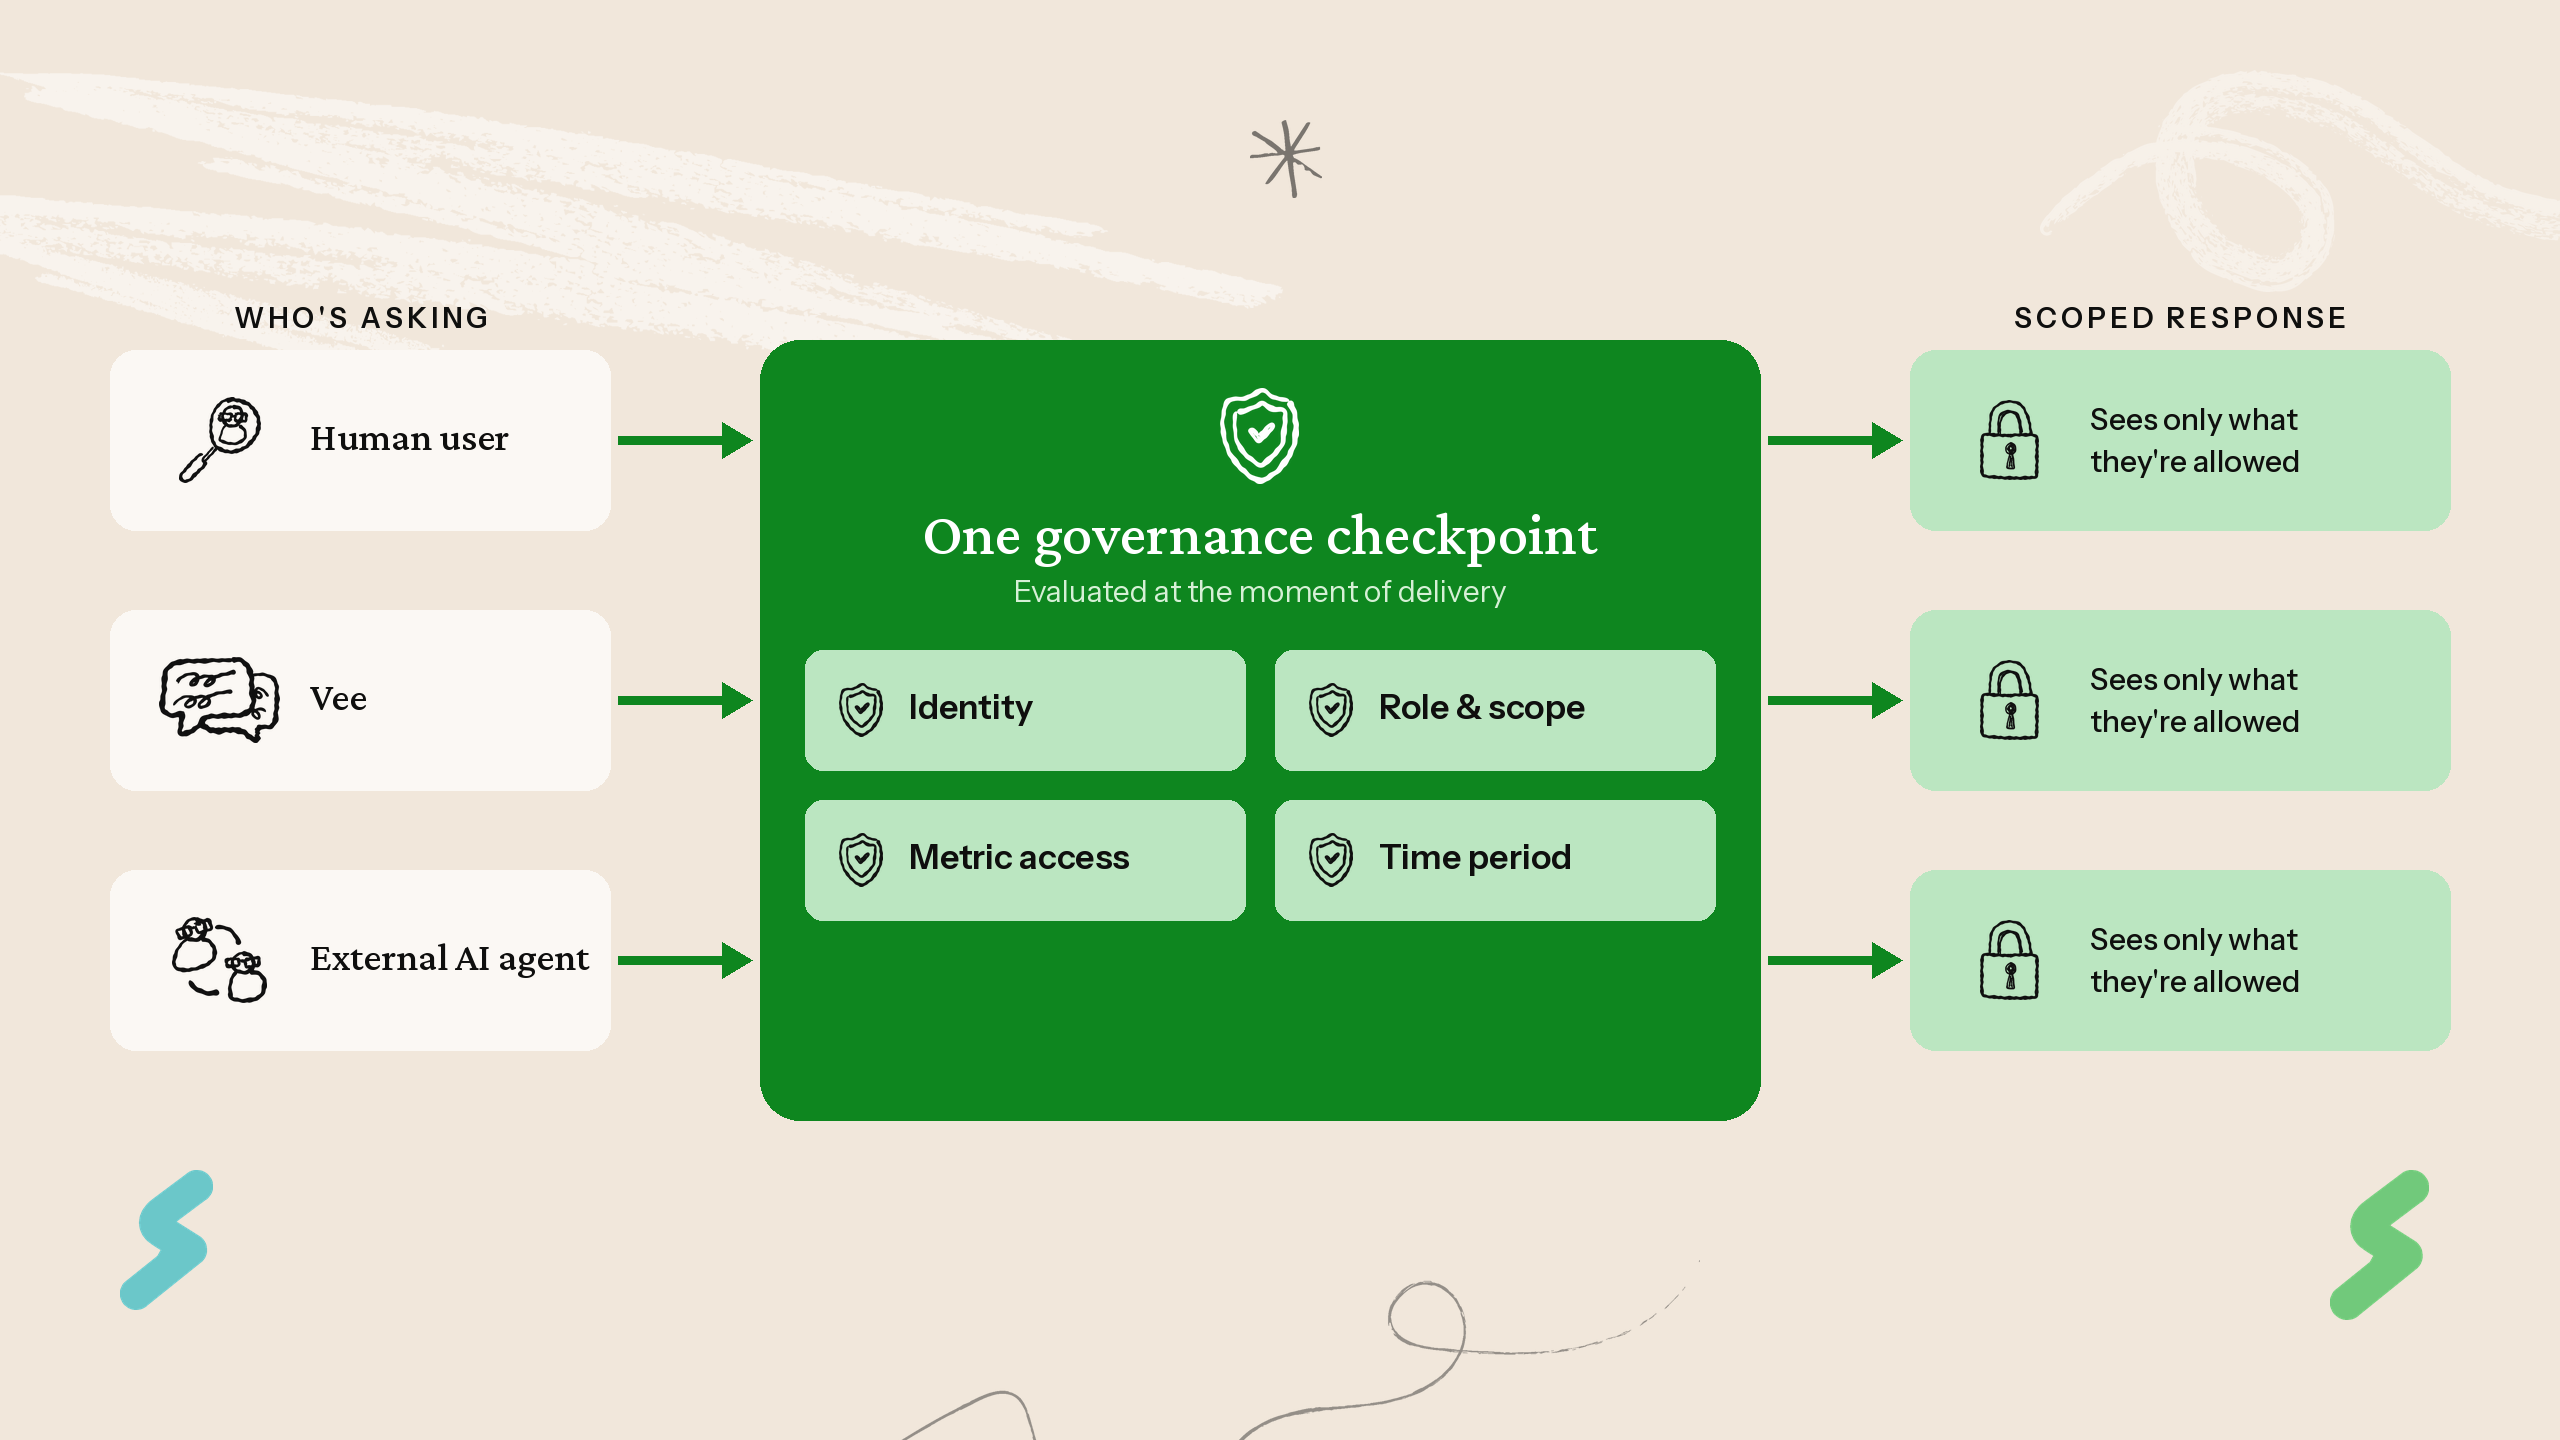
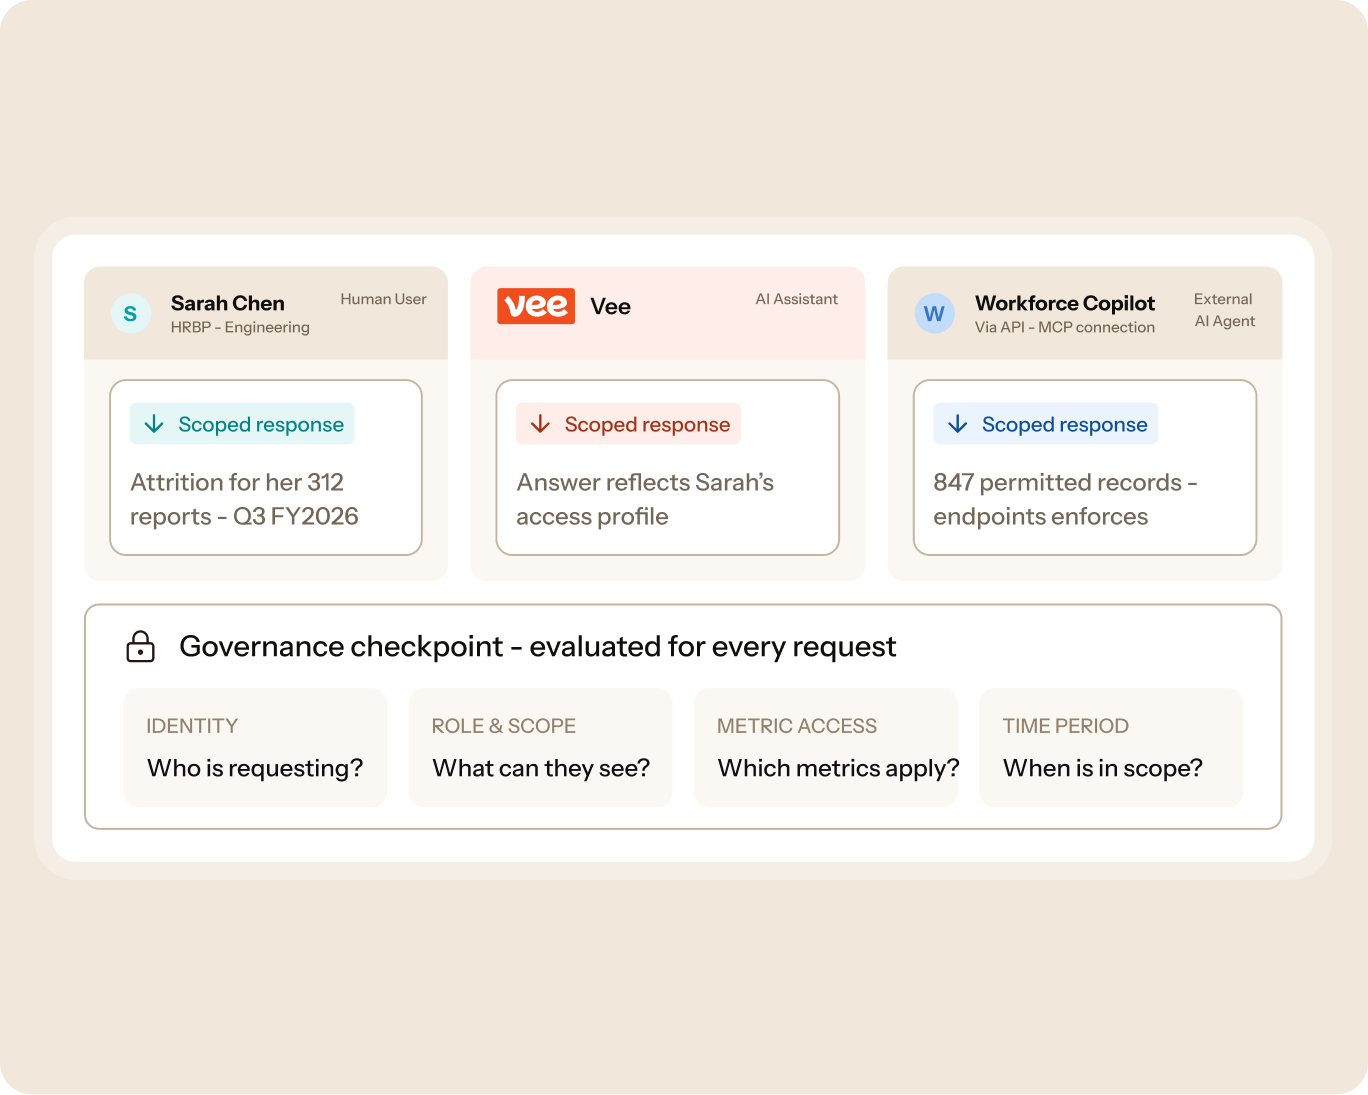
Every request for workforce data is evaluated at the moment of delivery: who's asking, what they can see, which org structure applies, what time period is in scope. When someone changes roles, their access changes with them.
The same model applies to AI agents. Visier’s agents, such as Vee, see only what the user is authorized to see. An external AI agent through MCP inherits the permissions of the user. Any additional new channels inherit the rules that already exist.
ACCESS AND PERMISSIONS
One security model to manage across all surfaces
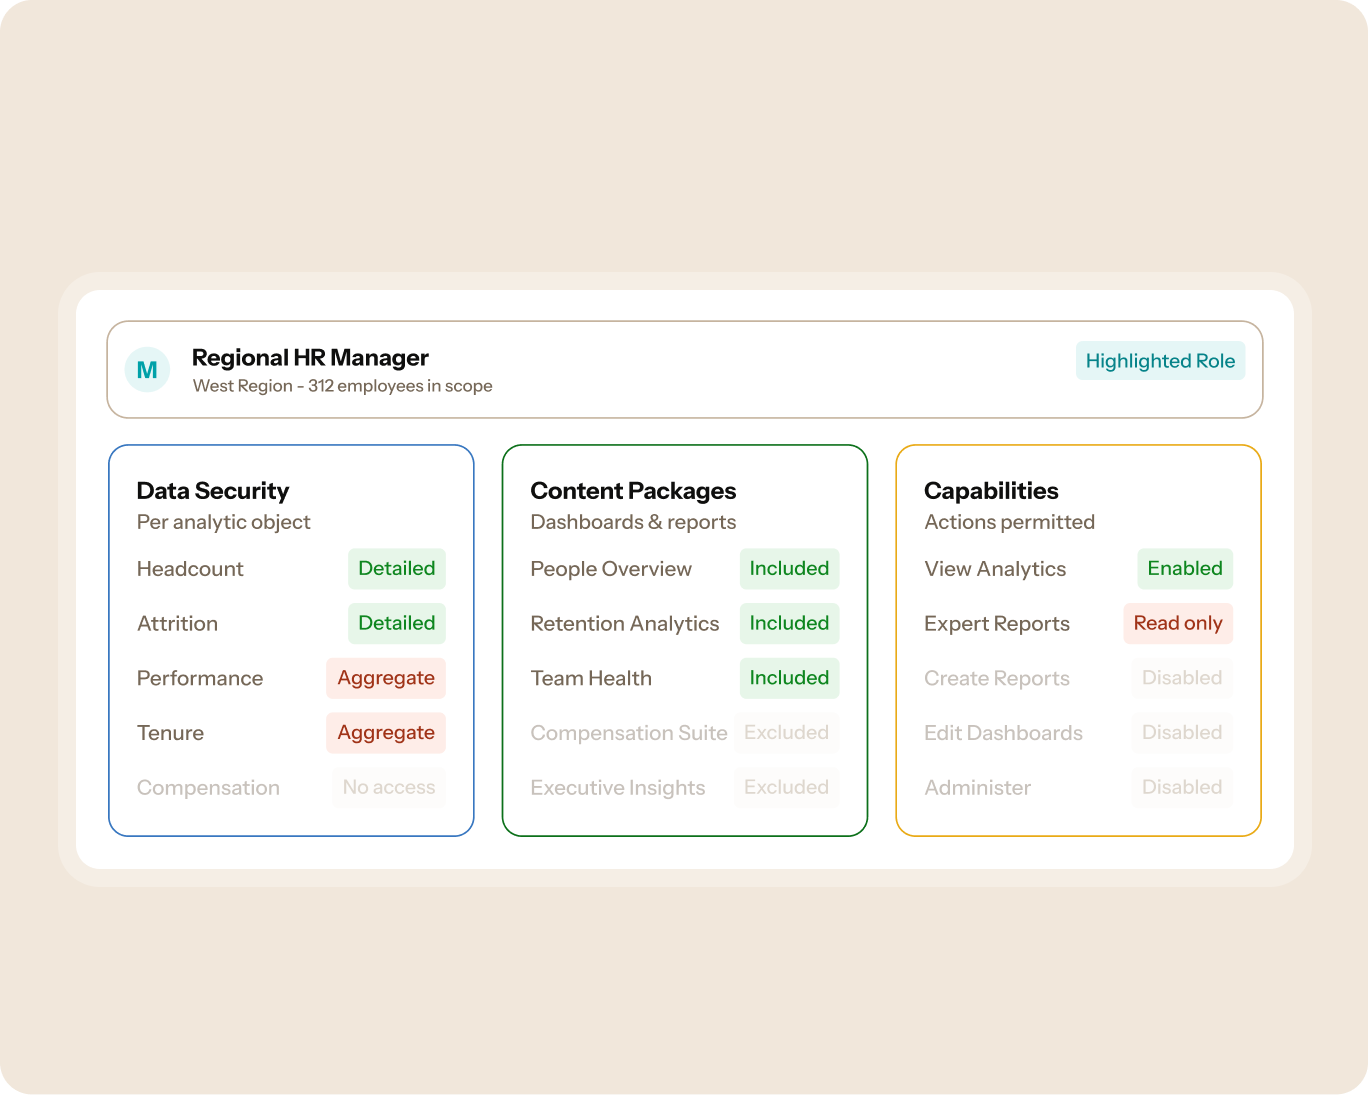
Access is governed across three dimensions. Data Security controls visibility per analytic object at detailed, aggregate, or no-access levels. Content Packages control which analytics a user sees. Capabilities control what actions they can perform.
Every user or agent sees exactly what they're authorized to see, at the right level of detail, and nothing more. Permissions stay in sync automatically through your regular data feed. User provisioning integrates with your existing IAM via SCIM, SSO, or API.
Review our security documentation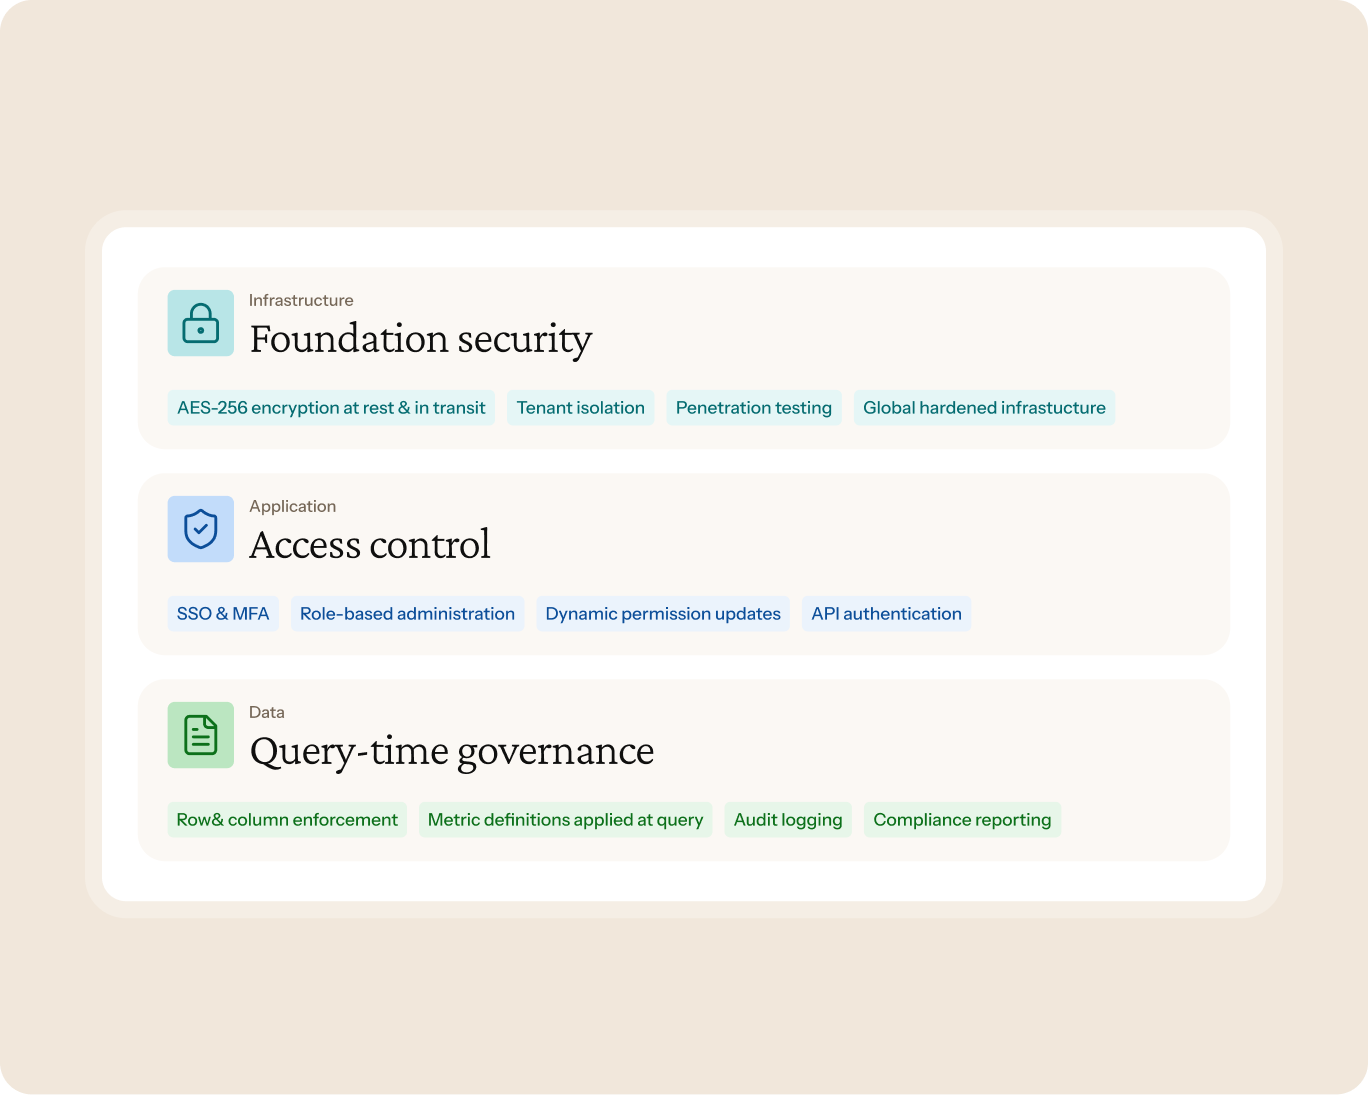
DATA PROTECTION
Encrypted, isolated, auditable.
Visier encrypts data at every stage. Customer environments are logically isolated. And access controls are enforced at the application layer, not just the infrastructure layer.
AES-256 encryption at rest, TLS 1.2+ in transit
Logical tenant isolation
SSO and MFA integration
Audit logging for every data access event across all users and agents
Artificial Intelligence
Visier Research: Strategic Workforce Planning in the AI Era
New Visier research reveals the 5 critical gaps between AI ambition and readiness for large enterprises—and how to close them

Governed, secure, makes IT happy